

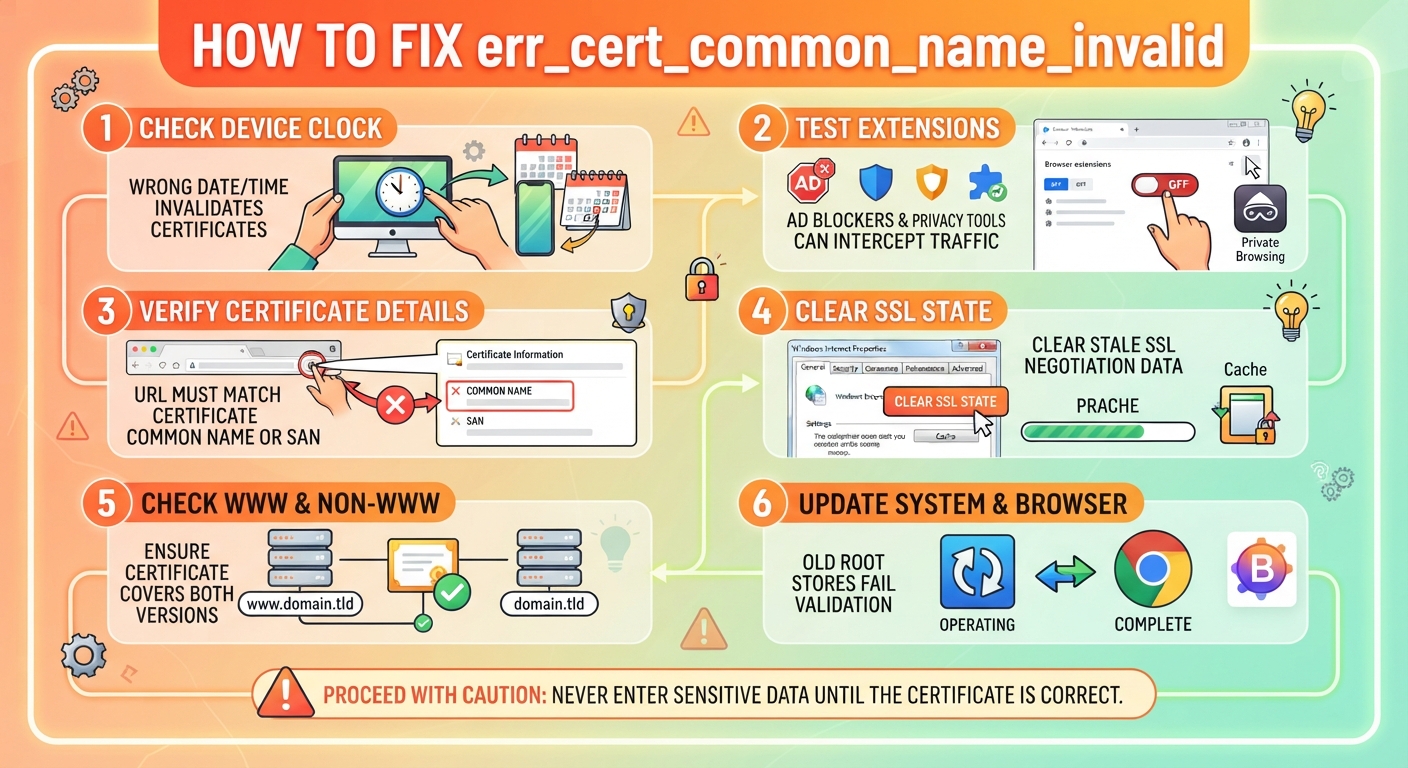
A blocked page and the string err_cert_common_name_invalid usually point to one thing. The name on the certificate does not match the name you typed. Chrome, Edge and every other Chromium browser stop the connection right there.
Most cases trace back to the server. A few trace back to your own machine. Below is how to tell them apart, and what to change in each case.
What err_cert_common_name_invalid Means
Every SSL certificate lists the hostnames it covers in two fields: the common name and the Subject Alternative Name entries. Your browser compares that list against the address bar.
No match, no handshake. The warning appears before a single byte of page content loads, which is why refreshing rarely helps.
The message is not proof of an attack. Interception looks identical to a sloppy install, so the browser treats both the same way.
What Causes err_cert_common_name_invalid
| Origin | Typical fault |
|---|---|
| Web server | Certificate omits the exact host or subdomain requested |
| Your device | Wrong clock, stale SSL cache, odd proxy values |
| Third-party software | Extension, firewall or antivirus intercepting traffic |
Check the Date and Time on Your Device
Certificates carry a validity window. A clock that drifts by months makes every one of them look wrong, and the browser reports the mismatch instead of the real cause.
Open your system settings and correct both the date and the time zone. On Linux, timedatectl shows the current state and sets it. A full restart of the machine clears the last of the cached negotiation data.
Certificates that sit outside their window throw a related warning, err_cert_date_invalid, which needs a different repair.
Test Extensions That Trigger err_cert_common_name_invalid
Ad blockers and privacy tools inspect encrypted traffic, and a broken one breaks the chain of trust. Load the site in a private window first, since extensions stay off there by default.
Chrome and Edge
Open the three-dot menu, pick More tools, then Extensions. Switch each one off, reload, and stop when the page opens.
Firefox and Safari
Firefox keeps the same controls under Add-ons and themes. Safari hides them in Settings, then Extensions. Remove whichever one fails the test.
Read What the SSL Certificate Actually Covers
The common slip is fitting a certificate issued for one hostname onto another. A file bought for www.domain.tld does nothing for shop.domain.tld.
Click Not Secure at the left of the address bar, choose Certificate, and read the issued-to row. From a terminal, openssl s_client -connect domain.tld:443 prints the same fields with more detail.
Self-signed files belong on internal machines only. If a local test box needs one, pair it with your own dnsmasq resolver so the hostname you sign is the hostname you request. When the domain fails to resolve at all, you get err_name_not_resolved instead.
Cover Both www and Non-www Versions
Many single-domain certificates guard both spellings. Some do not. Redirecting traffic from one to the other then hands visitors a name the certificate never listed.
| Certificate type | What it covers |
|---|---|
| Single domain | One hostname, usually with and without www |
| Wildcard | A domain plus one level of subdomains |
| Multi-domain | Several unrelated hostnames on one file |
Pick the type that matches your redirect map, or drop the redirect.
err_cert_common_name_invalid on WordPress Sites
A frequent cause is forcing HTTPS in the site settings with no certificate installed at all. WordPress will happily rewrite every URL to https:// and let the browser fail.
Issue a certificate through your hosting control panel and bind it to the domain. Rolling the site back to HTTP also clears the error, but it leaves traffic unencrypted.
Clear the SSL State and Browser Cache
Browsers hold certificate data between visits. After a new install on the server, the old record can still be in play.
On Windows, open Internet Properties, switch to the Content tab, and press Clear SSL state. Chrome routes to the same panel through its proxy settings. Cache trouble also shows up as err_cache_miss on form submissions.
Review Proxy and Firewall Settings
A proxy that terminates TLS presents its own certificate, and that certificate rarely carries the site name. Open LAN Settings, tick Automatically detect settings, and reload.
Corporate networks and reverse proxy setups often terminate SSL one hop before the origin, so check which host holds the certificate. On Linux, review your nftables rules before blaming the browser.
Antivirus suites scan HTTPS the same way. Read the log before disabling anything, because the block may be correct.
Update the Browser and Operating System
Old builds ship old root stores. A certificate signed by a newer authority then fails validation on a machine that has not seen an update in years.
Chrome, Edge, Opera and Brave all share the same Blink engine, so a fix in one arrives in the rest. Run the system updater too, since the root store lives there.
FAQs
What does err_cert_common_name_invalid mean?
The hostname in the address bar is missing from the certificate’s common name and SAN list. Chrome treats that gap as a failed identity check and stops the page before any data moves.
How do I bypass err_cert_common_name_invalid in Chrome?
Click Advanced, then Proceed. Where policy hides that link, typing thisisunsafe on the warning page works. Use it only on servers you own, because the connection stays unverified.
Is err_cert_common_name_invalid dangerous?
Usually it is a setup mistake rather than an attack. Even so, never enter passwords or card details on a site showing this warning until the certificate lists the exact hostname.
Why does Reddit suggest checking the clock first?
Threads in r/techsupport land on that fix because a wrong system date invalidates every certificate at once. If several unrelated sites break together, correct the clock before touching the server.
Does a wildcard certificate fix err_cert_common_name_invalid?
Only for one level of subdomains. A file for *.domain.tld covers shop.domain.tld but not api.shop.domain.tld. Reddit sysadmin threads flag that second-level gap as a repeat offender.
