

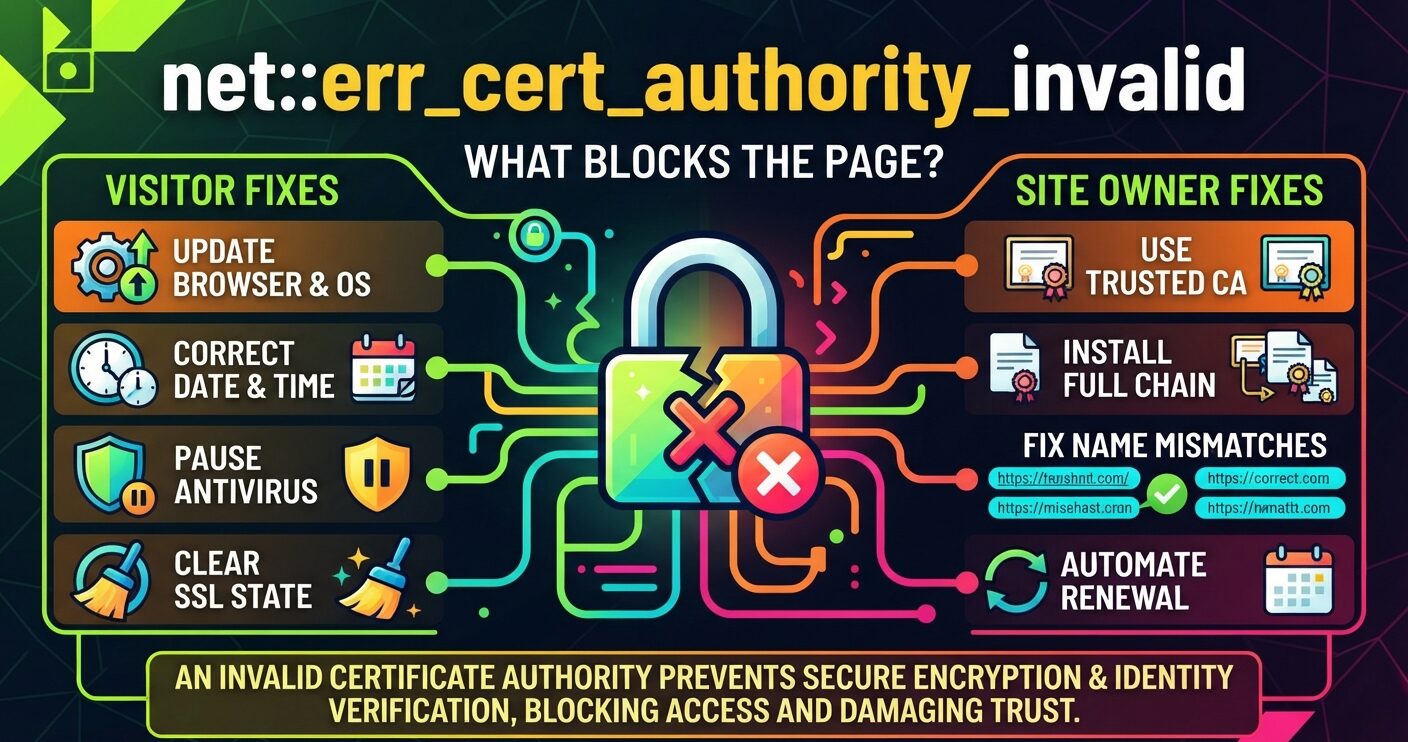
A browser that shows net::err_cert_authority_invalid has refused to trust a site’s SSL certificate. The page stays blocked because nothing proves the server is genuine or that your traffic stays encrypted.
Sometimes the fault sits on your own device. Other times the site owner shipped a broken setup. The fixes differ for each side, so both are covered below.
What Does net::err_cert_authority_invalid Mean?
The browser could not trace the site’s certificate back to an issuer it trusts. Every certificate needs a chain of signatures ending at a root authority stored on your machine.
Software reads those roots from a trusted file or folder, the same way OpenSSL sets its CA verify locations. No matching root means no proof of identity.
That puts passwords and card numbers at risk of reaching a stranger. Developers hit the same wall on local test servers and in-house tools.
What Causes the net::err_cert_authority_invalid Error?
Self-Signed or Unrecognised Issuer
Browsers accept certificates only from issuers on their approved list. A file the owner signed alone works for a test box, never for a live shop.
Debian’s make-ssl-cert wrapper produces this kind of certificate. Fine for a lab. Useless in public.
Expired or Revoked Certificates
Certificates last between three and twelve months. Issuers also pull ones that get abused.
A wrong device clock causes the same failure. The check reads your machine’s time, not the server’s.
Name Mismatch or Bad Server Config
A certificate for example.com does not cover www.example.com. Wildcards like *.example.com span subdomains, but names still have to line up.
Odd Apache or NGINX directives can break an otherwise valid file too.
Missing Intermediate Certificates
Trust runs from your certificate through middle files up to a root. Drop the middle and nothing completes the check. The OpenSSL verify command reference shows how each link gets tested.
Outdated Browser or OS
Root lists and cipher support change often. Old builds reject newer certificates they cannot read.
How net::err_cert_authority_invalid Looks in Different Browsers
Chrome shows “Your connection is not private” with the code underneath. Other browsers word it their own way, and the first thing to try changes too.
Chrome
Clear all-time browsing data under Settings > Privacy and Security. Disable extensions, restart, then open the padlock viewer to inspect the certificate.
Safari
Remove stored data under Preferences > Privacy > Manage Website Data. Check that the Keychain entry is set to trusted, then update Safari.
Arc
Clear the site’s cached data, switch off extensions, and reset Arc to its defaults.
How to Fix net::err_cert_authority_invalid as a Visitor
Start with the cheap checks. Most visitor-side cases trace back to a device setting.
1. Update the Browser and OS
Fresh root stores arrive with system and browser updates. Patch both first.
2. Correct Your Date and Time
Turn on automatic time sync (NTP) and confirm your time zone. On Linux, timedatectl set-ntp true switches it on.
After that, the systemd-timesyncd service keeps the clock from drifting again.
3. Test in a Private Window
Extensions and HTTPS-inspecting VPNs can trigger the block. If the page opens in private mode, disable add-ons one at a time. Then clear cache and cookies.
4. Pause Antivirus HTTPS Scanning
Some security suites decrypt your traffic and reseal it with their own certificate. Turn that feature off, restart, and test. Switch it back on afterward.
5. Clear the SSL State
On Windows, use the Clear SSL state button in the Content tab of Internet Options. On macOS, delete the site’s Keychain records.
Ubuntu users can clear entries from a terminal (Ctrl+Alt+T) or in Firefox under Settings > Privacy & Security > View Certificates. Reload the page.
6. Trust the Certificate Manually
Do this only for a site you control. Export the certificate through the padlock into your trusted store, or use Firefox’s certificate manager.
On Ubuntu, copy the .crt file into /usr/local/share/ca-certificates and run update-ca-certificates. You lose a safety check for that site, so keep it rare.
7. Contact the Site Owner
Still blocked? The fault likely lives on the server. Ask whoever runs the site to renew or reinstall the certificate.
How to Fix net::err_cert_authority_invalid as a Site Owner
Visitors who see the warning leave without buying. Traffic, ranking, and reputation drop together.
1. Use a Trusted Certificate Authority
DigiCert, GlobalSign, and Sectigo sell certificates. Let’s Encrypt issues them free, and Bluehost and SiteGround bundle one with hosting.
2. Install the Full Chain
Upload everything the issuer sent, not just your own certificate. Order matters: your certificate first, then intermediates, as the notes on loading a PEM certificate chain describe.
Qualys’ SSL test shows what your server hands to browsers.
3. Check the Installation
SSL Checker and Why No Padlock flag missing links and name clashes. Point Apache, NGINX, or IIS at the correct files.
4. Fix Name Mismatches
Reissue with exact hostnames after adding or dropping www. A wildcard or multi-domain certificate covers both spellings.
5. Automate Renewal
Certbot, ZeroSSL, and acme.sh handle issuing and renewal. Issuers email warnings, but a calendar reminder catches the ones that slip past.
6. Retest
Aim for an A grade or higher. Confirm that plain HTTP traffic lands on the HTTPS version.
Does net::err_cert_authority_invalid Hurt SEO?
Yes. Google rewards encrypted sites. A lingering certificate fault sends more visitors straight back to results and puts a “Not Secure” label in the address bar.
Related errors to rule out: err_cert_date_invalid, err_cert_common_name_invalid, and net::err_empty_response.
Is It Safe to Bypass net::err_cert_authority_invalid?
Only when you know the address is legitimate, like your own dev server. Sometimes the cause is minor. A drifting clock. A browser nobody updated.
Often it is a real problem, though. With free certificates and automatic renewal available, a live site in 2026 has no reason to show this warning.
FAQs
Is it safe to proceed past NET::ERR_CERT_AUTHORITY_INVALID?
Only if you control the site or know the address is genuine. The browser cannot confirm the server’s identity, so passwords and card details could reach an impostor.
How do I fix NET::ERR_CERT_AUTHORITY_INVALID in Chrome?
Update Chrome, sync your clock, clear all-time browsing data, and disable extensions. Then pause antivirus HTTPS scanning. If it still fails, the site owner must fix the certificate.
Why does NET::ERR_CERT_AUTHORITY_INVALID appear on every website?
A device problem is the usual cause: a wrong system clock, an outdated root store, or antivirus software resealing HTTPS traffic with its own certificate.
Can I trust Reddit fixes for net::err_cert_authority_invalid?
Check any Reddit fix against the cause first. Clock, cache, and antivirus changes carry little risk. Reddit advice to click through the warning or install unknown root certificates does, unless the site is yours.
Does a free SSL certificate cause NET::ERR_CERT_AUTHORITY_INVALID?
No. Browsers trust Let’s Encrypt certificates. The error comes from self-signed files, missing intermediates, expiry, or name mismatches, not from price.
