

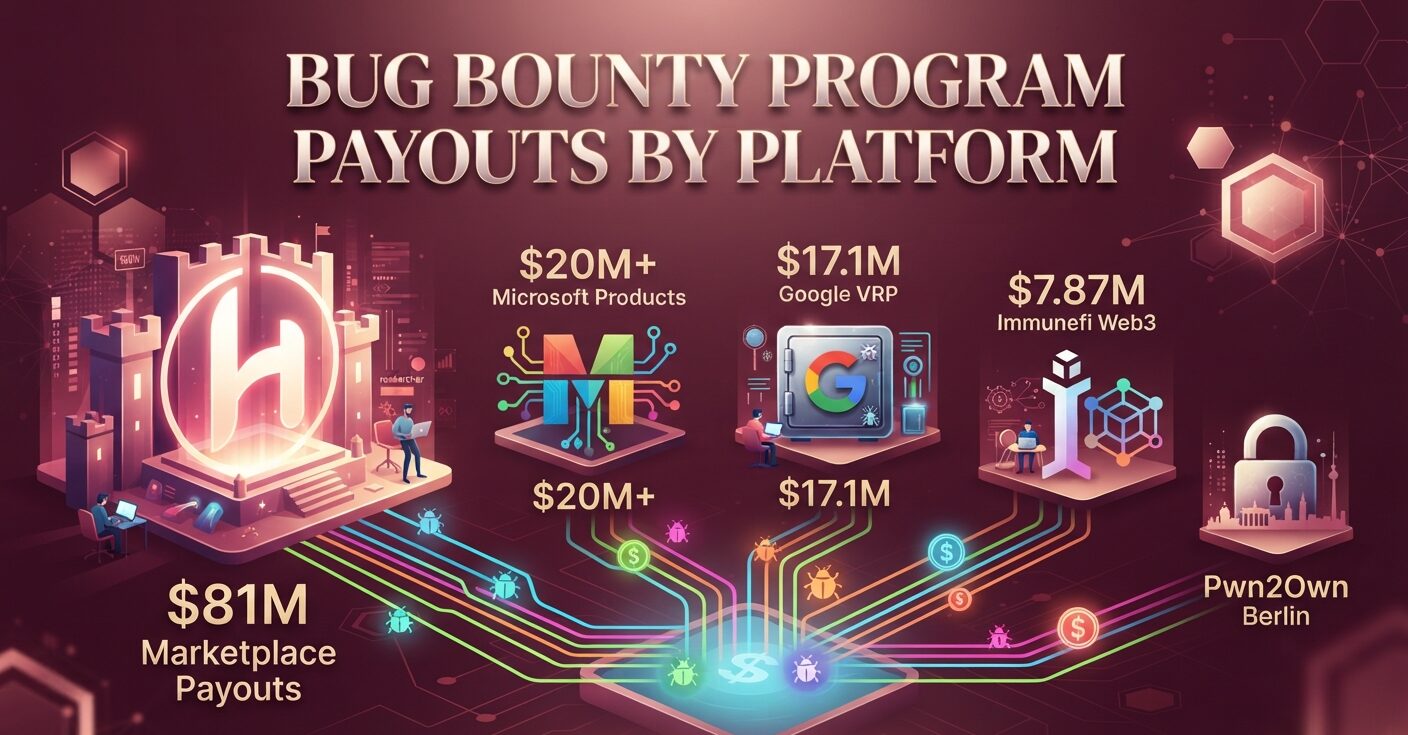
HackerOne’s latest report puts marketplace payouts at $81 million, while Microsoft paid more than $20 million for its own products alone. The two figures measure different scopes, and each platform reports on its own calendar. This guide sets out bug bounty program payouts by platform, covering marketplaces, vendors, Web3 and live contests, with the period and publisher attached to every number.
Bug Bounty Program Payouts by Platform
Which Platform Reported the Largest Bug Bounty Payout Total?
HackerOne reported the largest published total: $81 million paid between July 1, 2024 and June 30, 2025. That sum covers more than 1,950 customer programs, not a single company.
Source: HackerOne, Hacker-Powered Security Report (9th edition), July 2024 to June 2025
Microsoft paid more than $20 million to 562 researchers between July 1, 2025 and June 30, 2026. The money covers Microsoft products only.
Source: Microsoft Security Response Center, Bounty Program year in review, July 2025 to June 2026
Google’s Vulnerability Reward Program paid $17.1 million to 747 researchers in calendar 2025.
Source: Google, VRP 2025 Year in Review, calendar 2025
Immunefi, the Web3 marketplace, paid $7,872,078 to researchers in one quarter, Q1 2026.
Source: Immunefi, Ecosystem 2026 Q1 Update, Q1 2026
Meta awarded over $4 million in bug bounties during 2025.
Source: Meta Bug Bounty, 15th anniversary post, November 2025
These totals use different periods, so they appear side by side rather than as one ranking. Marketplaces report across all customer programs, while vendors report only what they paid for their own software.
HackerOne’s $81 Million Split Across 1,950+ Programs
The 100 highest-paying HackerOne programs paid $51 million of the $81 million total. The top 10 programs alone paid $21.6 million.
| HackerOne payout measure | Amount (USD) |
|---|---|
| All bug bounty programs | $81 million |
| Top 100 programs | $51 million |
| Top 10 programs | $21.6 million |
| Average yearly payout per active program | About $42,000 |
Source: HackerOne, Hacker-Powered Security Report (9th edition), July 2024 to June 2025
Total payouts rose 13% year over year. HackerOne counted 1,121 programs with AI in scope, up 270%, and more than 560 valid reports from autonomous AI agents.
HackerOne estimates its programs helped avoid nearly $3 billion in losses. For published breach costs by sector, see breach cost figures across industries.
Source: HackerOne, Hacker-Powered Security Report (9th edition), 2025
Bug Bounty Program Payouts on Immunefi, Quarter by Quarter
Immunefi paid researchers $7,872,078 in Q1 2026, up 228% from $2,399,948 in Q4 2025. Its cumulative researcher payouts passed $134 million by the end of March 2026.
Q1 2026 Against Q4 2025
| Immunefi metric | Q4 2025 | Q1 2026 |
|---|---|---|
| Total paid to researchers | $2,399,948 | $7,872,078 |
| Paid bug bounty reports | 953 | 1,104 |
| Average payout per report | $2,518 | $7,131 |
| Unique researchers paid | 355 | 403 |
| Active programs (period end) | 218 | 230 |
Source: Immunefi, Ecosystem 2026 Q1 Update, Q4 2025 and Q1 2026
One payout drove much of the jump. A single $3 million award made up 38% of all Q1 2026 researcher payouts, and the top five reports summed to about $4.5 million.
Source: Immunefi, Ecosystem 2026 Q1 Update, Q1 2026
What Does a Critical Bug Pay on Immunefi?
Immunefi programs have paid $107.3 million for confirmed critical vulnerabilities. The median critical payout is $20,000; the mean is $114,355.
The study covers 593 bug bounty programs from January 2021 to February 2026, with audit competitions excluded. Its high end includes a $10 million Wormhole payout, which Immunefi calls one of the largest single awards in DeFi.
Among programs live five years or longer, 93.9% have logged at least one confirmed, paid critical disclosure.
Source: Immunefi Research, program data January 2021 to February 2026 (published April 2026)
How Much Did Microsoft Pay Researchers in FY2026?
| Microsoft Bounty Program | July 2024 to June 2025 | July 2025 to June 2026 |
|---|---|---|
| Total awarded | $17 million | More than $20 million |
| Researchers awarded | 344 | 562 |
| Researcher countries | 59 | 64 |
Source: Microsoft Security Response Center, Bounty Program year-in-review posts, FY2025 and FY2026
MSRC calls the latest year the highest total payout in the program’s history. It received 2,531 eligible reports through 15 bounty programs, and the largest single award was $200,000.
The Zero Day Quest live hacking event accounted for $2.3 million. Expanded scope covering third-party and open source code produced more than 300 additional reports and over $800,000 in awards.
Microsoft said submission volume rose notably from January to June 2026 and attributed part of that to researchers using AI. Rewarded reports end up as fixes, and patch release timelines by operating system show how quickly vendors ship them.
Source: Microsoft Security Response Center, August 2026
Google VRP: $17.1 Million Across 747 Researchers in 2025
Google paid $17.1 million through its Vulnerability Reward Program in 2025, which it calls an all-time high and more than 40% above 2024. The highest single reward was $250,000.
Total VRP awards since the program started in 2010 reached $81.6 million.
Invite-only bugSWAT live hacking events added concentrated payouts. The Cloud edition in Sunnyvale produced 130 reports and $1,600,000 in rewards.
The AI bugSWAT in Tokyo yielded 70+ reports and over $400,000. Las Vegas produced 77 reports and $380,000, and Mexico City 107 reports and $566,000 to date.
Source: Google, VRP 2025 Year in Review, calendar 2025
Pwn2Own Berlin 2026 Payouts by Day and Team
Pwn2Own Berlin 2026 awarded $1,298,250 for 47 unique zero-days over three days in May 2026. Day one paid $523,000 for 24 bugs, day two $385,750 for 15, and day three $389,500 for eight.
| Team | Master of Pwn points | Winnings (USD) |
|---|---|---|
| DEVCORE | 50.5 | $505,000 |
| STARLabs SG | 25 | $242,500 |
| Out Of Bounds | 12.75 | $95,750 |
Source: Trend Micro Zero Day Initiative, Pwn2Own Berlin 2026 results, May 14 to 16, 2026
Two exploits earned $200,000 each. DEVCORE’s Cheng-Da Tsai chained three bugs for SYSTEM-level code execution on Microsoft Exchange.
STARLabs SG’s Nguyen Hoang Thach took the other $200,000 for a VMware ESXi memory corruption exploit. ESXi hosts are a frequent target, as ransomware data split by operating system shows.
Red Hat Enterprise Linux for Workstations was also exploited on day three. Broader kernel exposure is tracked in these Linux malware and vulnerability numbers.
Source: Trend Micro Zero Day Initiative, Pwn2Own Berlin 2026, May 2026
What Do Meta and Apple Pay Bug Bounty Hunters?
Meta awarded over $4 million in 2025, up from over $2.3 million in 2024. Across 15 years, it has paid more than $25 million to over 1,400 researchers from 88 countries.
Source: Meta Bug Bounty, 2024 review (February 2025) and 15th anniversary post (November 2025)
Apple has paid over $35 million to more than 800 researchers since its public bounty launched in 2020. Multiple individual reports earned $500,000.
From November 2025, Apple’s top award doubled to $2 million for zero-click exploit chains. Bonuses for Lockdown Mode bypasses and beta-software bugs can lift the maximum above $5 million.
Source: Apple Security Research, Apple Security Bounty update, October 2025
Bugcrowd Reports a 32% Rise in Critical Bug Bounty Payouts
Bugcrowd’s latest CISO report gives a percentage change rather than a dollar total. Average payouts for critical vulnerabilities rose 32% across 2024.
The same report counted an 88% rise in hardware vulnerabilities and a doubling of network vulnerabilities. Critical broken access control findings rose 36%, and critical sensitive data exposure findings rose 42%.
Those are counts of submitted findings, not payouts. For how often public flaws reach critical scores, see the Linux CVE severity breakdown.
Source: Bugcrowd, Inside the Mind of a CISO 2025 (published September 2025), 2024 platform data
FAQs
Which bug bounty platform pays the most?
HackerOne reported the largest published total: $81 million from July 2024 to June 2025, across more than 1,950 programs. Microsoft ($20 million+) and Google ($17.1 million) report only payouts for their own products.
How much does a critical bug pay on Immunefi?
The median critical payout is $20,000 and the mean is $114,355, based on 593 Immunefi bug bounty programs from January 2021 to February 2026.
Is bug bounty hunting worth it, as Reddit threads often ask?
Published data shows payouts are concentrated. On Immunefi, one $3 million award made up 38% of Q1 2026 payouts. No platform cited here publishes a median annual income per researcher.
How much did Google pay bug hunters in 2025?
Google paid $17.1 million to 747 researchers through its Vulnerability Reward Program in 2025. The largest single reward was $250,000.
What is the biggest bug bounty payout?
Immunefi has paid a $10 million award for a Wormhole bug, which it calls one of the largest in DeFi. Apple’s top listed award is $2 million, rising above $5 million with bonuses.
Sources
https://www.hackerone.com/report/hacker-powered-security
