

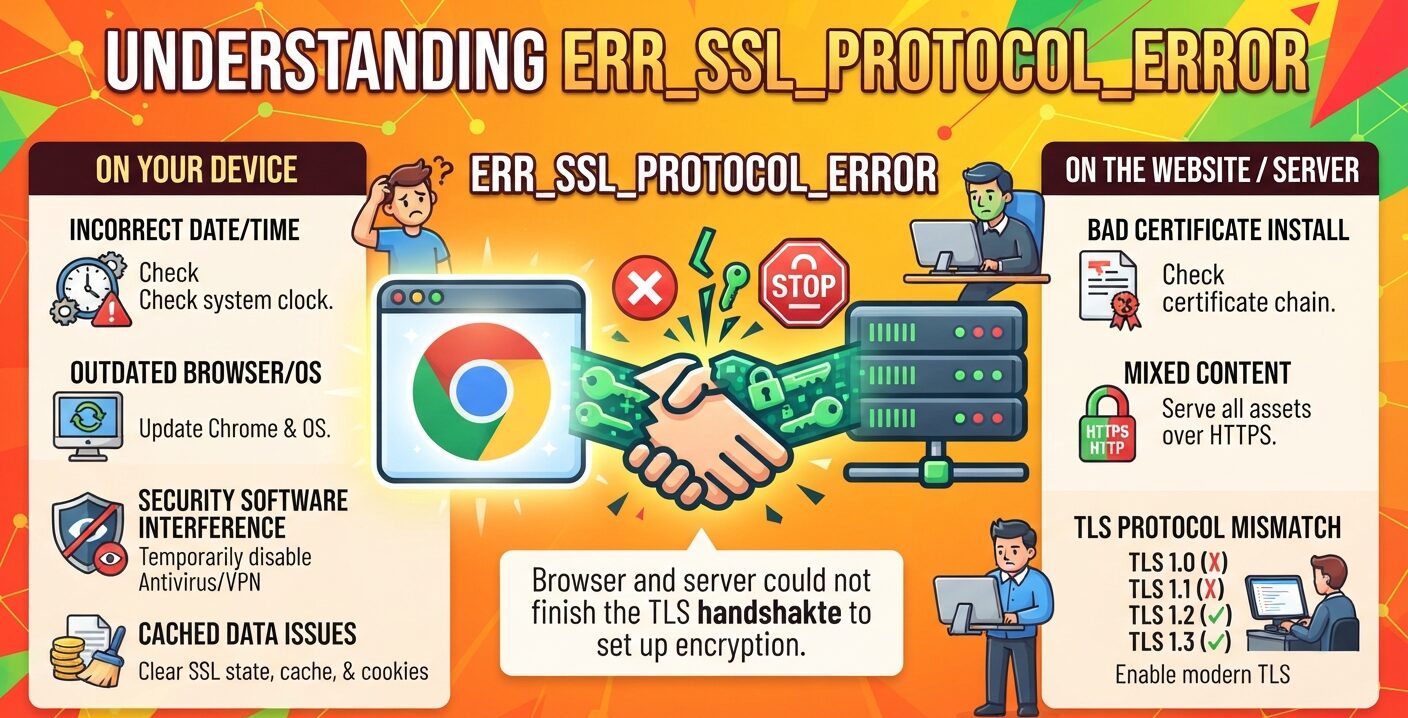
You click a link, and Chrome shows a grey page instead of the site. ERR_SSL_PROTOCOL_ERROR means your browser and the web server could not finish the TLS handshake.
That handshake is the short exchange that sets up encryption. Nothing loads until it works. The fault sits on your device or on the server, and a two-minute test tells you which.
What ERR_SSL_PROTOCOL_ERROR Means in Chrome
Chrome prints the code under the heading “This site can’t provide a secure connection.” The line above it often says the site sent an invalid response.
Behind the screen, the browser and server tried to agree on a TLS version, a cipher and a set of keys. They failed. SSL is the older name for this system, and TLS replaced it, though most people still say SSL.
Some certificate faults, like the one in our guide to expired or future-dated certificates, can offer an Advanced link. This screen has none. Chrome has no safe channel to fall back on, so it blocks the page outright.
Edge, Firefox and Safari Word It Differently
Edge, Brave and Opera run on Chromium, so they show the same code. Firefox opens a “Secure Connection Failed” page with its own SSL_ERROR code.
Safari skips codes. It says it can’t open the page because it could not set up a secure connection.
Is ERR_SSL_PROTOCOL_ERROR Coming From Your Device or the Website?
Run three checks before you touch any settings:
- Open the page in a second browser.
- Load it on your phone over mobile data, with Wi-Fi off.
- Visit any other HTTPS site on the first device.
A site that fails everywhere has a server problem. Only its owner can repair it.
A site that works on your phone but not your laptop points at the laptop. If every HTTPS page breaks, look at your network, VPN or security software first.
Other Chrome network errors split the same way. A page that never finds its address is a DNS fault, the kind behind err_name_not_resolved in Chrome.
Six Common Causes of an SSL Protocol Error
| Trigger | Where the fault sits | Typical sign |
|---|---|---|
| Badly installed certificate | Website | Domain mismatch, lapsed file, unknown issuer |
| Mixed HTTP and HTTPS files | Website | Padlock turns to a warning mid-load |
| Security software blocking traffic | Device or network | Error clears once protection pauses |
| Wrong date or time | Device | Valid certificates read as expired |
| Outdated browser or OS | Device | Current ciphers not supported |
| QUIC transport | Either side | Mismatch during the handshake |
Certificates cause most cases. A certificate issued for one domain fails on another, a problem close to err_cert_common_name_invalid. A certificate from an unrecognised issuer fails too.
Mixed content breaks trust in a quieter way. The page pulls some files over HTTPS and others over plain HTTP, so only part of the route is guarded.
Clocks matter more than people expect. Every certificate has a start and end date. A device set years ahead reads a healthy certificate as dead.
QUIC is a Google protocol built to speed up services such as YouTube and Gmail. It runs over UDP instead of TCP, and a bad setup throws the handshake out of step.
How to Fix ERR_SSL_PROTOCOL_ERROR in Chrome as a Visitor
Work down the list. Reload the page after each step.
1. Correct the Date and Time
Check the day, hour and time zone. Then switch on automatic time so the clock syncs with an internet time server and stops drifting.
2. Clear the SSL State in Windows
Search for Internet Options, open the Content tab and press Clear SSL state. This wipes saved certificate records that may be stale. Mac and Linux users can skip to step 3.
3. Delete Cached Files and Cookies
Press Ctrl+Shift+Delete, set the range to All time, and tick cookies plus cached images and files. Old cached data causes other Chrome faults as well, such as the err_cache_miss warning.
4. Update Chrome
Open chrome://settings/help and install any pending update. Old builds may not support the TLS versions a site now requires. Install system updates too.
5. Test in Incognito for Extension Conflicts
Incognito turns extensions off by default. If the page loads there, disable ad blockers and privacy add-ons one at a time. Extensions can also block responses outright, as with err_blocked_by_response.
6. Pause Antivirus HTTPS Scanning or Your VPN
Some security suites inspect encrypted traffic and break the handshake. Pause HTTPS scanning, reload once, and turn it back on.
If that fixes it, add the site to the allow list. Do the same test with any VPN or proxy.
7. Turn Off QUIC in chrome://flags
Type chrome://flags in the address bar and search for QUIC. Set Experimental QUIC protocol to Disabled, then press Relaunch. Daily browsing barely changes without it.
Site Owners: Clearing ERR_SSL_PROTOCOL_ERROR on the Server Side
Review recent config edits first. A domain may have changed while the certificate stayed the same, or the file may sit in the wrong folder.
Check the Certificate and Its Chain
Run the domain through Qualys SSL Labs. It grades the chain, TLS versions and ciphers. From a shell, openssl s_client -connect example.com:443 -servername example.com shows what the server sends.
A missing intermediate certificate breaks trust, a fault covered in our piece on net::err_cert_authority_invalid. Wildcard certificates need extra care.
Enable TLS 1.2 and 1.3
Drop TLS 1.0 and 1.1. In Nginx, set the ssl_protocols directive. In Apache, set SSLProtocol. Reload the server after saving.
Serve Every Asset Over HTTPS
Open DevTools and check the Console for mixed content warnings. One script or image called over plain HTTP is enough to break the page.
Keep Port 443 Open
A firewall that blocks 443 stops HTTPS before it starts. Our walkthrough on how to open a port in Linux with ufw or firewalld covers the commands.
FAQs
Can I bypass ERR_SSL_PROTOCOL_ERROR?
No safe bypass exists. Chrome offers no proceed link for this error. Fix your clock, cache, browser or security software. If the site fails on every device, only its owner can repair it.
How do I fix ERR_SSL_PROTOCOL_ERROR on Android?
Set date and time to automatic. Clear Chrome’s cache under Settings, Apps, Chrome, Storage. Update Chrome from the Play Store. Then switch between Wi-Fi and mobile data to test the network.
Can a VPN cause ERR_SSL_PROTOCOL_ERROR?
Yes. VPNs and proxies that filter or inspect encrypted traffic can break the TLS handshake. Disconnect, reload the page, and reconnect. If the error disappears, change VPN servers or settings.
Is ERR_SSL_PROTOCOL_ERROR a virus, as some Reddit posts suggest?
No. It marks a failed TLS handshake, not an infection. Malware that intercepts traffic can trigger it, so run a scan if every HTTPS site fails on one device.
Should I follow Reddit advice to switch off antivirus for this error?
Only as a short test. Pause HTTPS scanning, reload once, then turn protection back on. If the page loads, add that site to the allow list instead of leaving protection off.
