

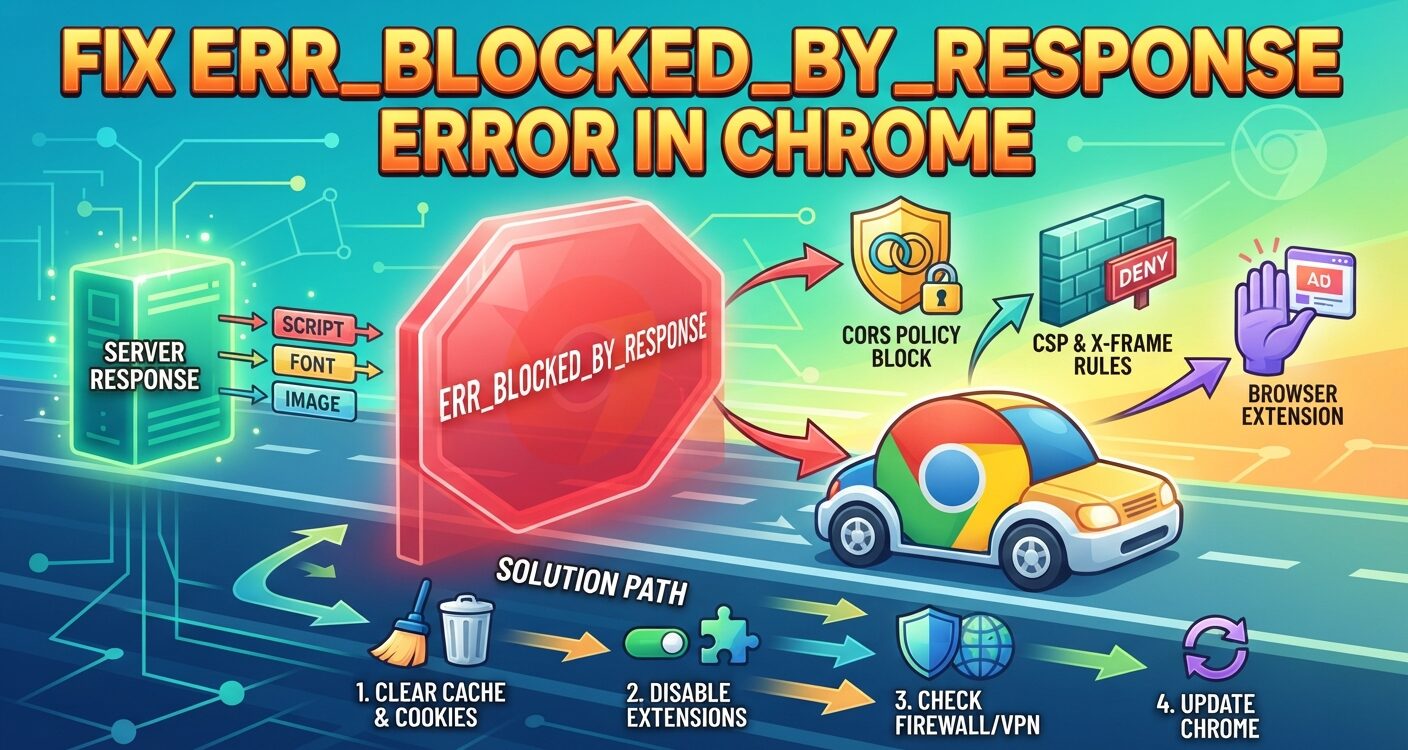
A tab that stalls and shows err_blocked_by_response has hit a rule, not a dead server. Chrome got a reply, then refused to use it.
The block can start in a site’s headers, a browser extension, or a filter on your network. Visitors can clear most cases in minutes. Site owners need DevTools and access to their server settings, so the fixes below are split by who can apply them.
What err_blocked_by_response Means in Chrome
Chrome shows this code once a security rule rejects what a server sent back. The server did answer. The browser then declined to load the file, whether a script, an image, a font or a style sheet.
That sets it apart from a reply that carries no data at all. With err_blocked_by_response, data reached Chrome and a policy stopped it.
You can meet the error in two places. Sometimes it fills the whole tab. More often it sits in the DevTools console as net::ERR_BLOCKED_BY_RESPONSE, beside a line that names the header at fault.
The NotSameOrigin and iframe versions
Chrome adds a suffix when it can name the rule. ERR_BLOCKED_BY_RESPONSE.NotSameOrigin means the file lives on another origin, and that server marked it for same-origin use.
Framed content breaks the same way. A form, video player or sign-in box inside an iframe fails if the embedded site sends X-Frame-Options: DENY, or a CSP frame-ancestors rule that leaves your domain out.
What Causes err_blocked_by_response? Five Common Sources
CORS headers missing on another domain
CORS decides whether one domain may pull files from another. Say your page loads a weather widget from api.weather.com. If that API never returns Access-Control-Allow-Origin with your domain, Chrome drops the reply.
Subdomains count as separate origins. A request from www.example.com to api.example.com needs the same permission, and only the API owner can grant it.
Strict CSP and X-Frame-Options rules
Content-Security-Policy lists the places allowed to supply scripts, styles and fonts. Anything off that list gets refused. A tight CSP can even stop Google Fonts.
Missing or wrong values in X-Frame-Options, Strict-Transport-Security or Content-Type lead to the same result.
Ad blockers and privacy extensions
uBlock Origin, AdBlock and Ghostery cut calls to known ad and tracker domains. Google Analytics tags and marketing pixels are frequent casualties.
Firewalls, VPNs and regional filters
Office firewalls, antivirus suites and country-level rules can refuse outside domains. That differs from Chrome’s offline error -106, where the browser finds no route and sends nothing.
A VPN can get around a regional block. Some VPNs add filters of their own, though.
Broken code in the request
A typo in JavaScript or a wrong API endpoint sends a malformed call. The server answers with a fault, and Chrome rejects the file.
How to Fix err_blocked_by_response in Chrome as a Visitor
Work down the list in order. The first two checks cost the least time.
1. Clear cached files and cookies
Stored files can clash with a site’s current rules. Press Ctrl+Shift+Delete, set the range to All time, tick cookies and cached files, then clear.
Stale storage breaks other things too, such as the err_cache_miss screen after a form submission. Reload the page once the wipe finishes.
2. Test Incognito, then switch off extensions
Open a private window with Ctrl+Shift+N and load the page. If it works there, an extension is the likely cause.
Go to chrome://extensions and turn each one off in turn, ad blockers first. Refresh after every change. If one blocker keeps breaking pages, this roundup of Manifest V3 ad blockers on Linux covers options with simpler allowlists.
Once you find the culprit, update it, remove it, or allowlist the site.
3. Pause the firewall, VPN or proxy
Disconnect the VPN and reload. Then pause the firewall for a moment and test again. A page that loads now points to the rule set, so adjust it and turn protection back on.
A proxy that terminates TLS can also produce certificate name mismatch warnings. On Windows, check Internet Options, then Connections, then LAN settings.
Antivirus HTTPS scanning deserves a look as well. It reseals traffic and can set off untrusted-certificate errors next to this one. Read its log before you disable anything.
4. Reset flags and update Chrome
Experimental settings can clash with site rules. Type chrome://flags, press Reset all, and relaunch.
Next, open Help, then About Google Chrome, and install any waiting update. A clean reinstall repairs a damaged build, and Linux users can follow this Chrome setup guide for Ubuntu.
Test the page again after the relaunch.
Fixing err_blocked_by_response on a Site You Manage
If every visitor sees the error, the fault sits on the server. No browser cleanup will help.
Read the blocked request in DevTools
Press F12, or right-click and choose Inspect. Open the Network tab and reload. Blocked requests show in red.
Click one and read its headers, status code and console note. Messages such as “No ‘Access-Control-Allow-Origin’ header is present” or “Refused to display in a frame” name the rule at fault.
Correct CORS, CSP and frame headers
Add Access-Control-Allow-Origin for each domain that needs your files. Add missing sources to the Content-Security-Policy. For iframes, set X-Frame-Options or frame-ancestors to allow the parent domain.
Most hosting panels expose these headers. Apache sites can set them in .htaccess. A CDN such as Cloudflare can rewrite headers too, so check its rules.
When a third-party server is at fault, you can’t change its headers. Send the blocked URL to its owner, or ask your host to trace the block.
err_blocked_by_response vs err_blocked_by_client
The two codes look alike but start in different places. err_blocked_by_client comes from your own machine. An ad blocker or security extension cuts the request before it leaves Chrome.
err_blocked_by_response means the reply arrived and a rule refused it. Server headers and network filters are the first suspects. DNS faults are a third case: Chrome shows err_name_not_resolved when it can’t find the site, so no response exists to block.
Check the exact code in the console before picking a fix.
FAQs
Is err_blocked_by_response a sign of malware?
No. The error means Chrome refused a file because a header, extension or network rule blocked the response. It does not signal a virus or a breach.
Can a VPN fix err_blocked_by_response?
Sometimes. A VPN helps when a network filter or regional block stops the response. It changes nothing when the cause is a CORS header, a CSP rule or a browser extension.
Why does the error appear in one browser but not another?
Each browser keeps its own extensions, cache and privacy settings. If one of them blocks the response, that browser alone shows the error. A clean load elsewhere points to your local setup.
What do Reddit users try first for err_blocked_by_response?
Reddit threads point to Incognito mode as the first test. If the page loads there, an extension is at fault. Developers on Reddit then check CORS and CSP headers in DevTools.
Why won’t Reddit load inside an iframe or embed?
Reddit pages send frame-blocking headers, so Chrome refuses to show them inside another site’s iframe. Ad blockers that stop Reddit scripts cause the same error. Open the link directly or use Reddit’s official embed code.
